
We use cookies
We use essential cookies to run this site. With your permission, we'd also like to use analytics cookies to see how the site is used, and functional cookies for chat and videos. Change your choice any time under Cookie settings. Read our Cookies Policy
AWS vulnerability scanning
Find misconfigurations and vulnerabilities across your AWS accounts
Connect AWS with read-only access. SeqOps checks your configuration continuously, ranks every finding by severity, and shows your team how to fix it. First results arrive within 24 hours.
- 14-day free trial
- Read-only cloud access
- First results within 24 hours
- Compute
- Storage
- Networking
- Identity
- Database
AWS moves faster than manual reviews
Every new bucket, security group and IAM policy changes your exposure. Native tools produce long lists across many consoles and regions. Small teams don't have time to work out which items matter.
The result is a backlog nobody owns. Risky settings stay in place because nobody sees them next to everything else. Audit preparation turns into a hunt through screenshots and exports.
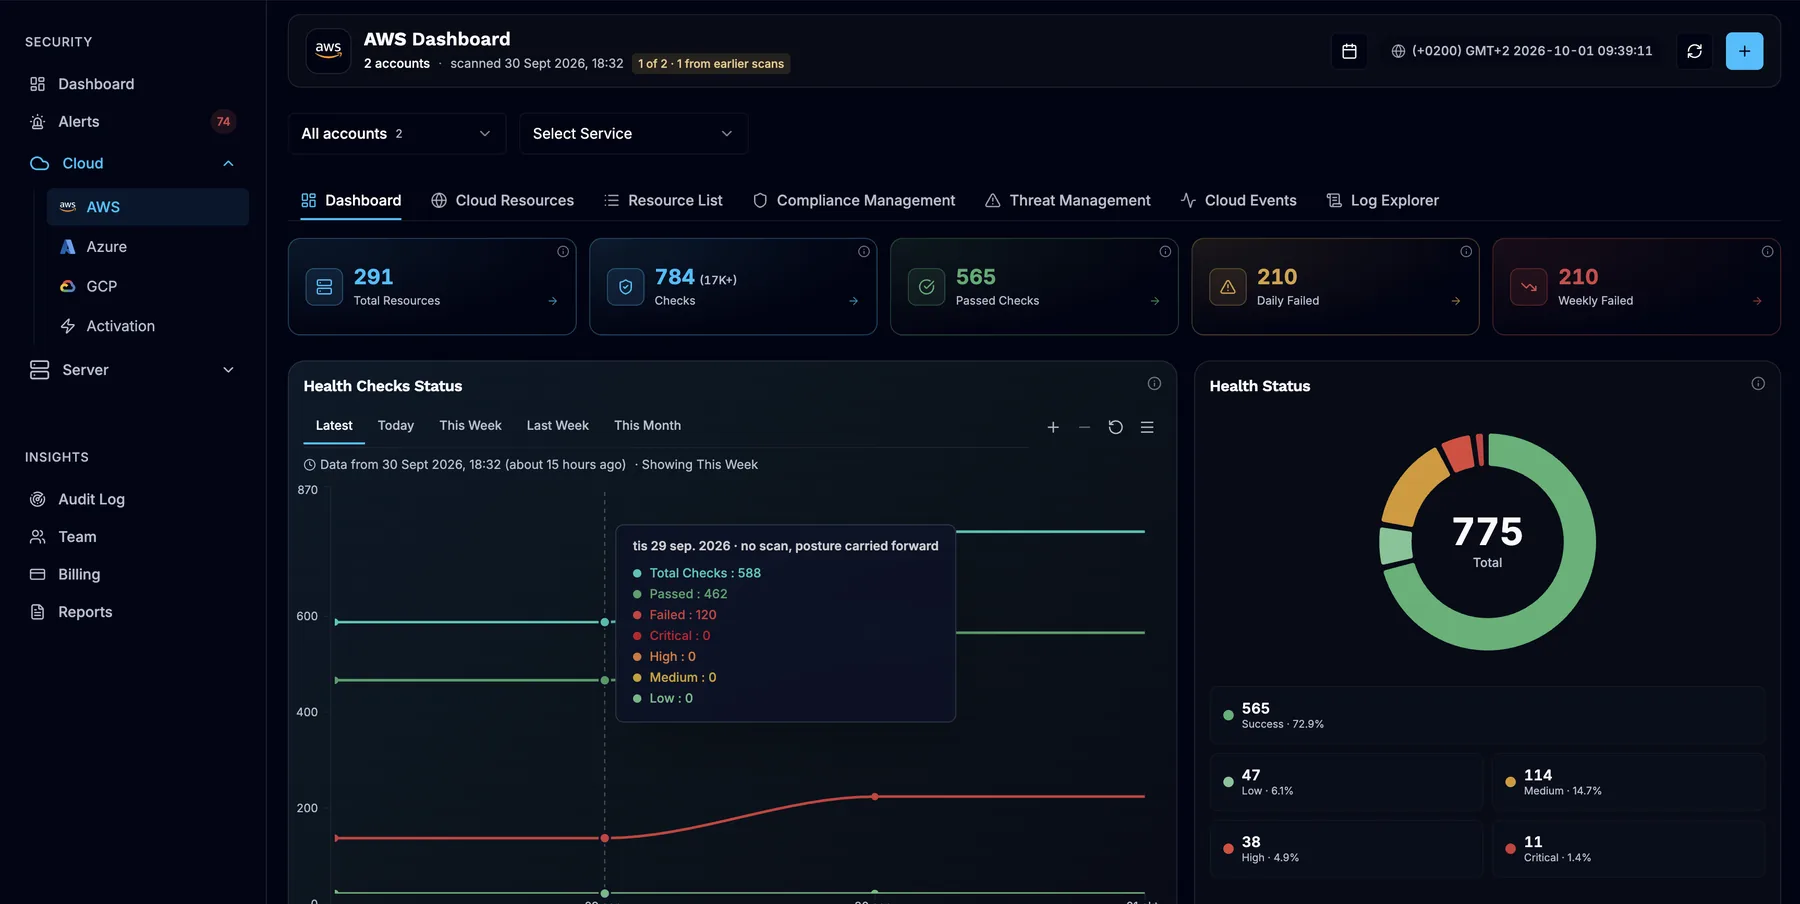
SeqOps brings the findings into one prioritised view, next to your Azure, Google Cloud and server results. Each finding has a severity, guidance on the fix and an owner you can assign.
What SeqOps checks
SeqOps builds an inventory of the resources in each connected AWS account. It then checks their configuration for vulnerabilities, misconfigurations and access risks.
- Compute resources and how they are configured
- Storage resources and their access settings
- Networking resources and their configuration
- Identity resources and the permissions attached to them
- Database resources and how they are configured
- Compliance checks from the AWS catalogue (25 entries), mapped to many compliance frameworks
- Installed software on EC2 instances that run the SeqOps agent (Windows or Linux)
- A severity for every finding: Critical, High, Medium, Low or Informational
Connect once, get results within 24 hours
Step 1: Create a read-only role
Create an IAM role with the SecurityAudit and ViewOnlyAccess policies, plus an IAM user that can assume it. Add the Access Key ID, Secret Access Key and Role ARN in SeqOps.
Step 2: SeqOps reads your configuration
Click Test Credentials, then save. SeqOps reads your configuration across regions. It builds an inventory of compute, storage, networking, identity and database resources.
Step 3: Review ranked findings
Within 24 hours of connecting (6–24 hours), findings appear ranked from Critical to Informational. Each one comes with guidance on how to fix it.
What you get
One prioritised list
SeqOps shows all your connected AWS accounts in one view, ranked by severity. Your Azure, Google Cloud and server findings sit in the same list. Accept a risk or mark a false positive when a finding doesn't apply.
Remediation guidance on every alert
Each alert explains the issue and how to fix it. AI-powered analysis adds a plain-language explanation and a suggested fix. Assign it to an owner and track it to Resolved. Send alerts to email, Slack, Microsoft Teams, Jira, ServiceNow or a webhook.
Compliance view by framework
See how your AWS configuration scores against the compliance frameworks in your plan. Review the controls that pass and fail, and the resources behind each failure.
Scheduled reports and exports
Scheduled PDF reports go out bi-weekly, weekly or daily, depending on your plan. Export findings as CSV, PDF or Excel for management and auditors.
Read-only by design
SeqOps uses a read-only IAM role with the SecurityAudit and ViewOnlyAccess policies. It can't create, change or delete anything in your AWS account.
It collects configuration metadata only, stored in AWS eu-north-1 (Stockholm). Connections use TLS in transit, and cloud credentials are encrypted before storage.
Sign-in to SeqOps supports multi-factor authentication. Compliance frameworks are the standards SeqOps checks against, not certifications held by SeqOps. Admin actions and partner sessions are recorded in each organisation's audit log.
Visit the Trust CenterFrequently asked questions
What permissions does SeqOps need in AWS?
Does SeqOps work with AWS Security Hub or GuardDuty?
How many AWS accounts can I connect?
Can SeqOps scan my EC2 instances for software vulnerabilities?
How soon will I see results?
Read the guides
Related on the platform
- Azure scanning
Read-only checks for misconfigurations and vulnerabilities in your Azure subscriptions.
- Server scanning
Find vulnerabilities on Windows and Linux servers with a lightweight agent.
See what’s exposed in your cloud and servers
Start your 14-day free trial and get your first results within 24 hours.