
We use cookies
We use essential cookies to run this site. With your permission, we'd also like to use analytics cookies to see how the site is used, and functional cookies for chat and videos. Change your choice any time under Cookie settings. Read our Cookies Policy
Trust Center
Security at SeqOps
You’re trusting us with a view of your infrastructure. Here’s exactly what we collect, where it lives and how we protect it.
Your environment
- Cloud accountsRead-only access
- ServersOutbound-only agent, HTTPS
;}.g{fill:%2371b8e0;}.h{fill:%2379b9e3;}%3c/style%3e%3cclipPath%20id='a'%3e%3cpath%20class='a'%20d='M0,484.068s12.436,7.444,19.464,11.49c1.16.668,5.341,3.472,6.136,3.928a2.846,2.846,0,0,0,2.51.766L0,474.07Z'%20transform='translate(0%20-474.07)'/%3e%3c/clipPath%3e%3c/defs%3e%3cg%20transform='translate(-0.894%20-0.516)'%3e%3cpath%20class='b'%20d='M28.039,0c7.11,0,11.221.185,14.807,6.324l5.811,11c3.639,6.232,1.785,9.091-1.854,15.323L45.31,35.2c-3.585,6.14-5.458,9.686-12.568,9.686l-8.088.228c-7.11,0-11.062.174-14.647-5.965L3.4,27.945c-3.639-6.232-.822-9.151,2.817-15.383L7.749,9.909C11.334,3.769,11.961.8,19.071.8Z'%20transform='translate(0%2026.347)%20rotate(-30)'/%3e%3cpath%20class='c'%20d='M15.892,1.307A5.228,5.228,0,0,0,11.377,3.9L2.02,19.921a5.235,5.235,0,0,0,0,5.273l9.357,16.022a5.228,5.228,0,0,0,4.515,2.592H34.736a5.228,5.228,0,0,0,4.514-2.592l9.357-16.022a5.235,5.235,0,0,0,0-5.273L39.25,3.9a5.228,5.228,0,0,0-4.514-2.592H15.892m0-1.307H34.736a6.535,6.535,0,0,1,5.643,3.239l9.357,16.022a6.535,6.535,0,0,1,0,6.591L40.379,41.875a6.535,6.535,0,0,1-5.643,3.239H15.892a6.535,6.535,0,0,1-5.643-3.239L.892,25.853a6.535,6.535,0,0,1,0-6.591L10.249,3.239A6.535,6.535,0,0,1,15.892,0Z'%20transform='translate(0.894%2025.83)%20rotate(-30)'/%3e%3cpath%20class='d'%20d='M0,1926.875l14.465,8.352.022-.012L0,1926.851Z'%20transform='translate(20.165%20-1881.678)'/%3e%3cpath%20class='d'%20d='M814.065,1215.87l.125-.067-.125-.072Z'%20transform='translate(-779.509%20-1183.13)'/%3e%3cg%20transform='translate(11.763%2011.436)'%3e%3cpath%20class='e'%20d='M28.11,500.251v-9.995L8.444,478.877l-3.5-2.825L0,474.069l10.51,11.854Z'%20transform='translate(8.387%20-465.688)'/%3e%3cg%20transform='translate(8.387%208.381)'%3e%3cg%20class='f'%3e%3crect%20class='a'%20width='28.11'%20height='26.182'/%3e%3c/g%3e%3c/g%3e%3cpath%20class='c'%20d='M835.071,18.012l8.383,9.8V13.232l-12.1-7.326-1.55-.895L821.5.215l6.748,10.232Z'%20transform='translate(-798.588%20-0.211)'/%3e%3cpath%20class='g'%20d='M0,433.688l8.312,4.786,1.2-.691-7.552-5.228Z'%20transform='translate(8.387%20-425.306)'/%3e%3cpath%20class='g'%20d='M81.046,0,81.02.011,72.477,4.944l-4.75,2.742,8.312,4.786,4.718-2.724.005,0,1.546.9,8.738,5.071,3.58,2.077L81.053,0Z'%20transform='translate(-58.142%200.004)'/%3e%3cpath%20class='c'%20d='M-34.4,1334.451l22.8,13.093a102.553,102.553,0,0,0-7.044-10.592,57.33,57.33,0,0,0-7.369-7.723L-34.4,1318.82Z'%20transform='translate(34.402%20-1305.159)'/%3e%3cpath%20class='h'%20d='M1050.279,1684.65l7.839,5.093,1.7-.987-8.354-4.792Z'%20transform='translate(-1023.324%20-1654.193)'/%3e%3cpath%20class='h'%20d='M14.415,1379.833l.073.042,8.656-5,1.377-.8,2.387-1.378-8.339-4.8-2.386,1.377-1.367.789-10.4-6L0,1361.519l6.879,8.741Z'%20transform='translate(8.386%20-1337.448)'/%3e%3c/g%3e%3c/g%3e%3c/svg%3e)
SeqOps
- Hosting
- AWS eu-north-1 (Stockholm, Sweden)
- Stored
- Not your application data
Access and data
Read-only access
Cloud accounts connect with read-only permissions. SeqOps can’t change your cloud environment.
Outbound-only agent
The server agent connects out over HTTPS on port 443 (Windows servers also use port 8443 while being provisioned). No inbound ports, no cloud credentials on the server.
Security metadata only
Configurations, software versions, security settings and results. Not your application data.
Hosting and sub-processors
Hosting
Amazon Web Services, eu-north-1 (Stockholm, Sweden).
Sub-processors
AWS (hosting), Stripe (payments), Sentry (error monitoring).
Company
SeqOps AB, Tynäsgatan 12 a, 652 16 Karlstad, Sweden.
Protection
Encryption in transit
TLS for all connections.
Secrets
Cloud credentials and agent secrets are encrypted before storage; passwords and API keys are stored as one-way hashes. Download links are signed and short-lived.
Sign-in
Multi-factor authentication with an authenticator app or email code.
Audit log
Each organisation’s admins can see who did what and when, including partner sessions.
Roles
Role-based access for the people in your organisation.
Your data, your control
Leaving SeqOps
Access is revoked the same day. You have 30 days to export your data, after which it’s deleted through an approved deletion process (suspended only under legal hold).
DPA
Our Data Processing Agreement is in the legal hub.
Partner access you can audit
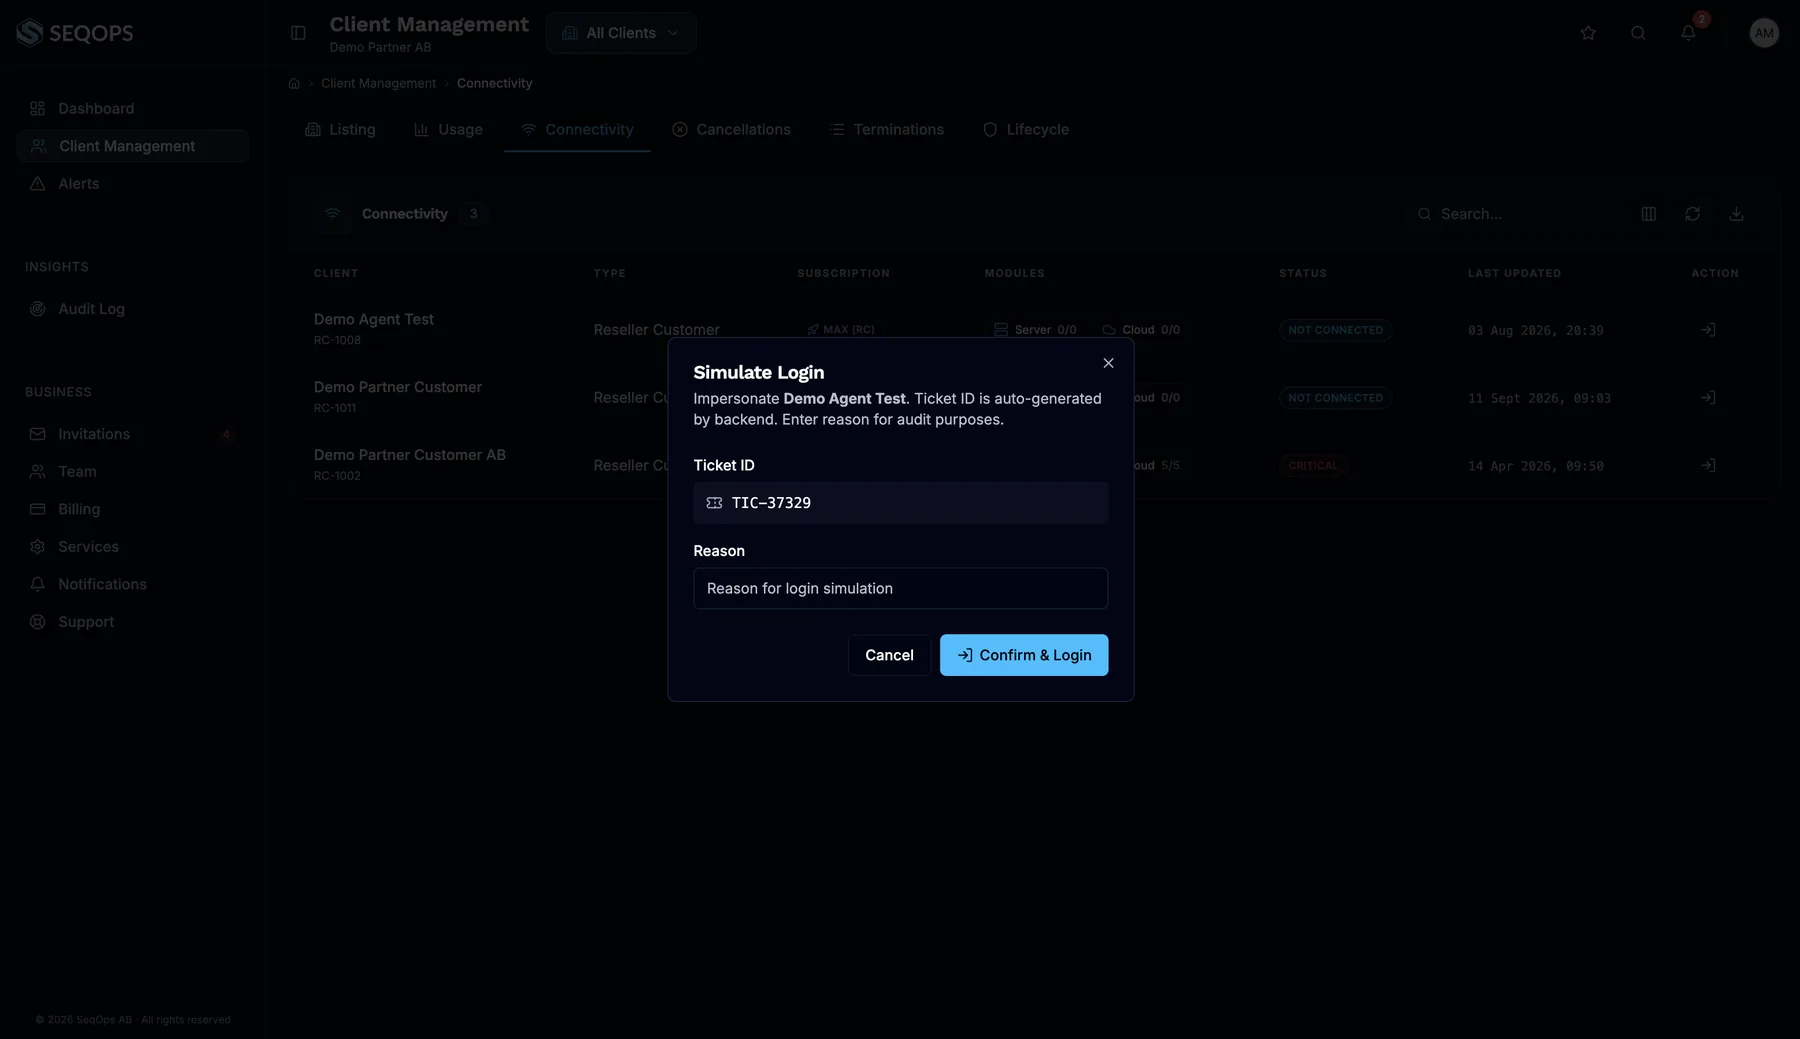
When a partner opens a customer workspace, SeqOps asks for a reason first. The session is recorded in the customer’s audit log.
Certifications and roadmap
SeqOps doesn’t hold SOC 2 or ISO 27001 certification today.
Our platform and processes are designed with those frameworks in mind.
Not yet offered: single sign-on (SAML/SSO) and SCIM provisioning, and a public status page.
Report a vulnerability
Found a security issue in SeqOps? Email support@seqops.io.
Machine-readable contact details: security.txt.